付款。
(在家觀看 = 0%,在校觀看 = 100%)
100% 在校觀看日期及時間:
自由選擇,點選以下地區觀看辦公時間及位置
課時: 30 小時
享用時期: 15 星期。進度由您控制,可快可慢。
課堂錄影導師:Larry
在校免費試睇:首 3 小時,請致電以上地點與本中心職員預約。
本課程提供在校免費重睇及導師解答服務。
(在家觀看 = 100%,在校觀看 = 0%)
100% 在家觀看日期及時間:
每天 24 小時全天候不限次數地觀看
課時: 30 小時
享用時期: 15 星期。進度由您控制,可快可慢。
課堂錄影導師:Larry
在校免費試睇:首 3 小時,請致電以上地點與本中心職員預約。
本課程提供導師解答服務。
Palo Alto Networks 是一家全球性的網路安全公司,總部位於美國。該公司成立於 2005 年,旨在提供最先進的網路安全技術,幫助客戶保護其網路不受惡意軟體、網路攻擊和資料外洩的侵害。
Palo Alto Networks 開發和提供一系列網路安全解決方案,包括下一代防火牆 (Next Generation Firewall)、雲端安全 (Prisma Cloud)、網路安全分析 (Cortex XDR) 和端點保護 (Endpoint Protection)等。
這些解決方案都基於自主研發的技術,如安全規則 (Security Policy)、威脅情報 (Threat Intelligence)和自動化安全控制等 (Cortex XSOAR),以確保客戶的網路安全。
Palo Alto Networks 的客戶包括全球範圍內的企業、政府機構、教育機構和服務提供商等。
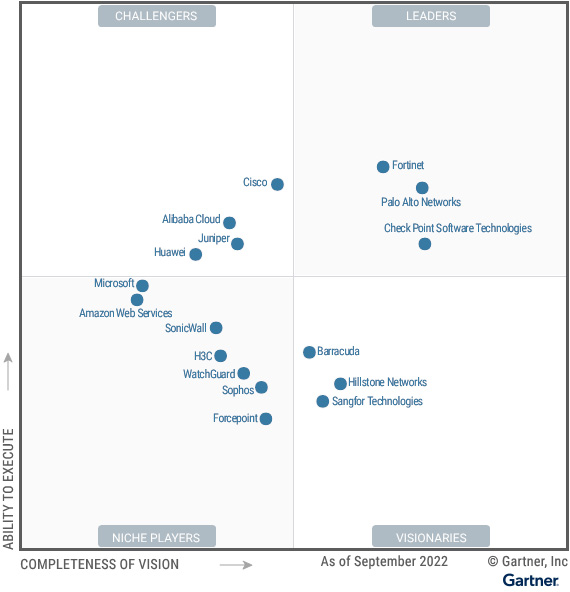
Palo Alto Networks 在全球擁有多個研發中心和辦事處,僱用了數千名員工,是網路安全行業的三大領導者之一,詳見以下 Gartner - Magic Quadrant for Network Firewalls:
作為一家致力於網路安全的公司,Palo Alto Networks 注重推動網路安全的創新和發展,與業內其他公司和組織合作,共同應對不斷出現的網路威脅。
Palo Alto Networks 的市值約為 1250 億美元 (超過 9750 億港元),該公司股價亦由 5 年前約 24 美元猛升至現在近 200 美元,是全球網路安全行業的領先企業之一。
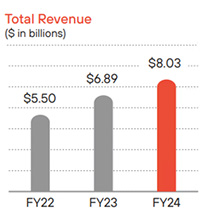
根據該公司的年度財報數據顯示,其全年營收為 80 億美元,較上年同期增長 16.5%;毛利約為 59 億美元。
Palo Alto Networks 在網路安全市場佔有相當大的市場份額,特別是在下一代防火牆 (Next Generation Firewall) 和網路安全分析等領域表現優異。
據市場研究機構 IDC 最近的報告顯示:
- Palo Alto Networks 在 <<全球防火牆市場份額>> 排名第一,市場佔有率為 22.4%;
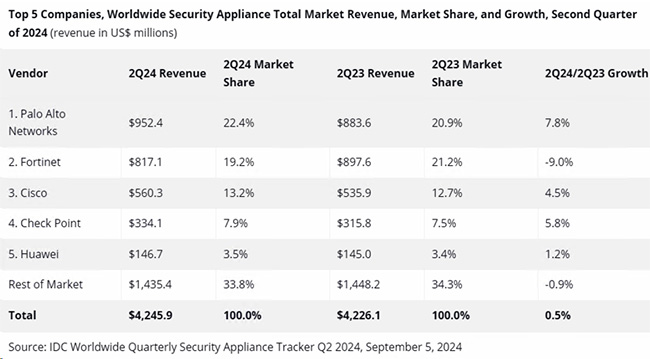
總體而言,Palo Alto Networks 在網路安全行業擁有穩健的財務狀況和強大的市場地位,並持續通過技術創新和業務拓展來推動其在市場中的競爭力。
Palo Alto Networks 的核心技術:PAN-OS (本課程的主要內容)
PAN-OS 基於專用硬體 (包括 PA 系列 Next Generation Firewall) 和虛擬化平台 (包括 VM 系列及 CN 系列),提供了一系列網路安全解決方案,包括下一代防火牆、雲端安全、網路安全分析和端點保護等。PAN-OS 擁有一系列先進的功能,包括:
- 智能防火牆:利用深度學習 (Machine Learning powered) 和人工智慧 (Artificial Intelligence) 技術,對網路流量進行實時分析和辨識,並能夠自動學習和調整防火牆規則。
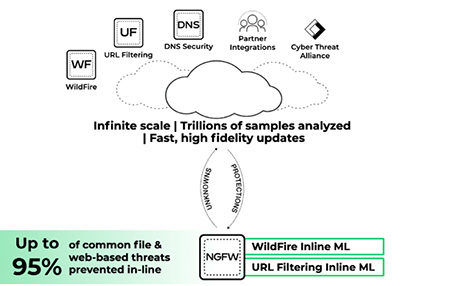
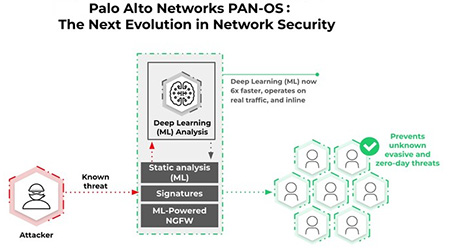
- 安全分析:Palo Alto WildFire 將大量的網路安全數據進行收集和分析,以便及時發現和應對各種威脅,包括惡意軟體、網路攻擊和資料外洩等。
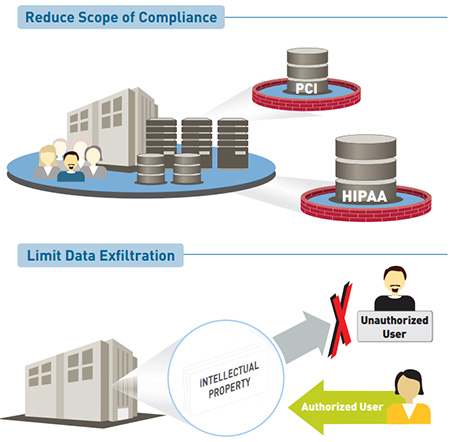
- 網路分段:通過分割網路流量,使得各個部門或用戶之間的流量互相隔離,以減少威脅的擴散和風險的傳播。
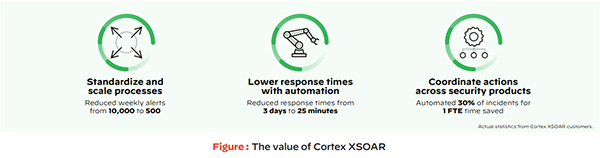
- 自動化安全控制:通過自動化技術,可以自動化執行安全操作,如阻止網路流量、隔離感染主機和防止資料外洩等。
Palo Alto Networks PA/VM/CN 系列防火牆是高度集成和自動化的技術,可以有效地防止網路受到各種尖端的威脅,如病毒、惡意軟件等。
獲得 Palo Alto Networks Certified Next-Generation Firewall Engineer 認證的人士,展示了他們具備有操作 Palo Alto Networks 下一代防火牆來保護網路免受尖端網路威脅的能力。
| 課程名稱: |
Palo Alto Networks Certified Next-Generation Firewall Engineer 國際認可證書課程 - 簡稱:Palo Alto Networks Firewall Training Course (提供 7x24 實習器材) |
| 課程時數: | 合共 30 小時 (共 10 堂) |
| 適合人士: | 對電腦網路安全有基本認識或有志投身 I.T. 界的人士 |
| 授課語言: | 以廣東話為主,輔以英語 |
| 課程筆記: | 本中心導師親自編寫英文為主筆記,而部份英文字附有中文對照。 |
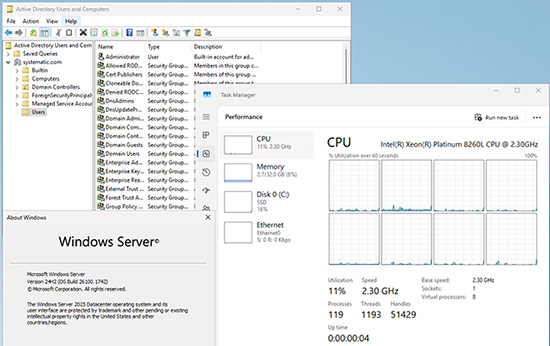
只要你於下列科目取得合格成績,便可獲 Palo Alto 頒發 Palo Alto Networks Certified Next-Generation Firewall Engineer 國際認可證書:
|
本中心為 Palo Alto Networks 指定的 NGFW-Engineer 考試試場,報考時請致電本中心,登記欲報考之科目考試編號 (即 NGFW-Engineer)、考試日期及時間 (最快可即日報考)。臨考試前要出示身份證及繳付考試費 HK$2,050。 考試題目由澳洲考試中心傳送到你要應考的電腦,考試時以電腦作答。所有考試題目均為英文,而大多數的考試題目為單項選擇題 (意即 O) 或多項選擇題 (意即 口)。作答完成後會立即出現你的分數,結果即考即知!考試不合格便可重新報考,不限次數。欲知道作答時間、題目總數、合格分數等詳細考試資料,可瀏覽本中心網頁 "各科考試分數資料"。 |
| 課程名稱:Palo Alto Networks Certified Next-Generation Firewall Engineer 國際認可證書課程 - 簡稱:Palo Alto Networks Firewall Training Course (提供 7x24 實習器材) |
1. Device Management and Services
1.1 Firewall Management Interfaces
1.1.1 Management interfaces
1.1.2 Methods of access
1.1.3 Web interface
1.1.4 Panorama
1.1.5 XML API
1.1.6 Access restrictions
1.2 Introduction to PANOS
1.2.1 App-ID
1.2.2 Content-ID
1.2.3 Device-ID
1.2.4 User-ID
1.2.5 WildFire Inline ML
1.3 Deploying the VM-Series Firewall
1.3.1 VM-Series Models
1.3.2 Supported Deployments on VMware vSphere
1.3.3 VM-Series on VMware System Requirements and Limitations
1.3.4 Plan the Interfaces for the VM-Series for ESXi
1.3.5 Deploying the OVA for practice
1.3.6 Perform Initial Configuration on the VM-Series on ESXi
1.4 Licensing
1.4.1 License Types
1.4.2 Flexible vCPUs and Fixed Model Licensing
1.4.3 Flexible vCPUs and Fixed Model Deployment
1.4.4 When licenses expire
1.5 Deploying Palo Alto VM-Series Next Generation Firewall on Clouds
1.5.1 About the VM-Series Firewall on Azure
1.5.2 Azure Networking and VM-Series Firewall
1.5.3 VM-Series Firewall Templates on Azure Cloud
1.5.4 Deployments scenarios supported on Azure Cloud
1.5.5 Deploy the VM-Series Firewall from the Azure Marketplace (Solution Template)
2. Network Segmentation with Interfaces and Zones
2.1 Designing Network Segmentation for a Reduced Attack Surface
2.1.1 Background
2.2 Configure Interfaces and Zones
2.3 Configure a Basic Security Policy between Zones
2.3.1 Background information and General concepts of Security Policy
2.3.2 Detailed Firewall Packet processing flow
2.4 Assessing Network Traffic
2.5 Service Route
3. Firewall Administration
3.1 Understanding the Candidate Configuration
3.2 Save and Export Firewall Configurations
3.2.1 Saving a local backup
3.2.2 Exporting Configurations
3.3 Restoring and Reverting Firewall Configuration
3.3.1 Revert to the current running configuration (file named running-config.xml).
3.3.2 Revert to a previous version of the running configuration that is stored on the firewall
3.3.3 Revert to Custom-named candidate configuration snapshot
3.3.4 Revert to a running or candidate configuration that you previously exported to an external host
4. Administrative Accounts
4.1 Administrative Role Types
4.1.1 Role Based
4.1.2 Dynamic
4.2 Configuring Admin Role Profile
4.3 Inside an Admin Role Profile Construction
4.4 Create and Configure Firewall Administrator Account
4.5 Configure Tracking of Administrator Activity
5. Zone Protection and DoS Protection
5.1 Packet Buffer Protection
5.1.1 Global Packet Buffer Protection
5.1.2 Per-Zone Packet Buffer Protection
5.1.3 Packet Buffer Protection Based on Buffer Utilization
5.2 Zone Attacks
5.3 Zone Defense Tools
5.3.1 Zone Protection profiles
5.3.2 DoS Protection profiles and policy rules
5.3.3 Summary
5.3.4 Firewall Placement for DoS Protection
5.4 Configuring and Applying a Zone Protection Profile
5.4.1 Flood protection in Zone Protection profile
5.4.2 Reconnaissance Protection in Zone Protection profile
5.4.3 Packet-Based Attack Protection
5.4.4 Protocol Protection
5.4.5 Ethernet SGT Protection
5.4.6 L3 & L4 Header Inspection
5.4.7 Configure Email notification for Alerts
5.5 DoS Protection Profiles and Policy Rules
6. App-ID
6.1 Introduction to App-ID
6.2 Streamlined App-ID Policy Rules
6.2.1 Create an Application Filter Using Tags
6.2.2 Background information about Decryption and APP-ID policy inspection
6.2.3 Keys and Certificates for Decryption Policies
6.2.4 Configuring SSL Decryption with SSL Forward Proxy
6.2.5 Creating a Decryption Policy rule
6.2.6 Verify Decryption
6.3 Decryption Exclusions
6.3.1 Reasons to Exclude Web sites from being decrypted by PA firewall
6.3.2 Palo Alto Networks Predefined Decryption Exclusions
6.3.3 Exclude a Web Site from Decryption for Technical Reasons
6.3.4 Exclude a Web Site from Decryption for Compliance and Privacy Reasons
6.3.5 Temporarily Disable SSL Decryption
6.3.6 Decryption Log
7. Security Profiles
7.1 Antivirus Profile
7.2 Anti-Spyware profiles
7.2.1 Default profile
7.2.2 Strict profile
7.3 Vulnerability Protection profiles
7.4 URL Filtering Profiles
7.5 Data Filtering Profiles
7.5.1 Creating a Data Filtering Profile
7.6 File Blocking Profiles
7.6.1 Basic file blocking
7.6.2 Strict file blocking
8. External Dynamic List
8.1 Introduction to External Dynamic List
8.2 EDL Types
8.2.1 Predefined IP Address
8.2.2 Predefined URL List
8.2.3 IP Address
8.2.4 Domain
8.2.5 URL
8.2.6 Equipment Identity
8.2.7 Subscriber Identity
8.3 EDL Formatting
8.3.1 IP Address List
8.3.2 Domain List
8.4 Built-in External Dynamic Lists
8.4.1 Palo Alto Networks Bulletproof IP Addresses
8.4.2 Palo Alto Networks High-Risk IP Addresses
8.4.3 Palo Alto Networks Known Malicious IP Addresses
8.4.4 Palo Alto Networks Tor Exit IP Addresses
8.5 Configure the Firewall to Access an External Dynamic List
8.6 Enforce Policy on an External Dynamic List
8.7 Retrieve an External Dynamic List from the Web Server
8.8 Using EDL Hosting Service feeds
9. Advanced WildFire
9.1 Introduction
9.2 Available subscription options
9.2.1 WildFire
9.2.2 Advanced WildFire
9.2.3 Standalone WildFire API
9.3 WildFire Features
9.3.1 Real-Time Updates
9.3.2 Five-Minute Updates (All PAN-OS versions)
9.3.3 Advanced WildFire Inline ML—(PAN-OS 10.0 and later)
9.3.4 File Type Support
9.3.5 Advanced WildFire API
9.3.6 WildFire Private and Hybrid Cloud Support
9.3.7 Intelligent Run-time Memory Analysis
9.4 Advanced WildFire Concepts
9.4.1 Samples
9.4.2 Firewall Forwarding
9.4.3 Advanced WildFire Analysis Environment
9.4.4 Advanced WildFire Inline ML
9.4.5 Advanced WildFire Verdicts
10. Managing Policy Objects
10.1 Address and Address Group Objects
10.1.1 How to tag objects
10.1.2 Address Object
10.1.3 Address Group object
10.2 Services
10.3 Application Filters
10.4 Application groups
10.5 Nesting application groups and filters
10.6 Application Characteristics
10.7 Policy Design and Evaluation
10.7.1 Create Security Policy Rules by App-ID instead of by Service
10.7.2 Rule Shadowing
10.7.3 Policy Usage statistics
10.7.4 Security Policy Rule Logging options
10.7.5 A Brief description of User-ID
10.7.6 Policy test match tool
10.7.7 Traffic Logging with Tap zone interface
10.7.8 Virtual Wire Interface
10.8 Layer2 vs Layer3 Interfaces
10.9 Sub-Interfaces
10.9.1 VLAN tags in conjunction with IP classifiers (address, range, or subnet).
10.10 Tunnel Interface
10.11 Aggregate interfaces
11. High Availability
11.1 Palo Alto HA Overview
11.2 HA Modes
11.2.1 Active/Passive
11.2.2 Active/Active
11.3 Failover Triggers
11.3.1 Heartbeat Polling and Hello messages
11.3.2 Link Monitoring
11.3.3 Path Monitoring
11.4 Floating IP Address and Virtual MAC Address
11.5 ARP Load-Sharing
11.6 Route-Based Redundancy
11.7 Firewall Session Owner
11.8 Firewall Session Setup
11.8.1 Session Setup Option
11.9 Prerequisites for Active/Passive HA
11.10 Configure Active/Passive HA
11.11 Verify Failover
12. Security in Quantum Computing Era
12.1 Quantum Security Concepts
12.2 Quantum Computing Threat
12.2.1 What Is A Quantum Computer?
12.2.2 How Does the Quantum Threat Affect My Network?
12.2.3 What to Do Now to Mitigate Harvesting Attacks
12.3 How RFC 8784 Resists Quantum Computing Threats
12.4 Support for Post-Quantum Features
12.4.1 RFCs Supported and Interoperability
12.4.2 HA Support
12.4.3 Upgrade and Downgrade Considerations
12.5 Post-Quantum Migration Planning and Preparation
12.5.1 Assign Resources and Build Awareness
12.5.2 Define Responsibilities
12.5.3 Develop a Crypto Inventory and Priority List
12.5.4 Evaluate Solutions, Experiment, and Test
12.5.5 Continue to Monitor Progress
12.6 VPN Configuration Best Practices
12.6.1 RFC 8784 Best Practices
12.6.2 RFC 9242 and RFC 9370 Best Practices
12.7 Configure Post-Quantum IKEv2 VPNs with RFC 9242 and RFC 9370 Hybrid Keys
13. GlobalProtect
13.1 Overview of GlobalProtect
13.2 Components of GlobalProtect
13.2.1 GlobalProtect Portal
13.2.2 GlobalProtect Gateways
13.2.3 GlobalProtect App
13.3 Basic Setup Concepts
13.3.1 Create Interfaces and Zones for GlobalProtect
13.4 Enable SSL Between GlobalProtect Components
13.4.1 About GlobalProtect Certificate Deployment
13.4.2 GlobalProtect Certificate Best Practices
14. Panorama
14.1 Panorama Overview
14.2 Panorama Models
14.2.1 Panorama virtual appliance
14.2.2 M-Series appliance
14.3 Centralized Firewall Configuration and Update Management
14.4 Context Switch—Firewall or Panorama
14.5 Total Configuration Size for Panorama
14.6 Centralized Logging and Reporting
14.7 Log Forwarding Options
14.8 Centralized Reporting
14.9 Forward Logs to Strata Logging Service
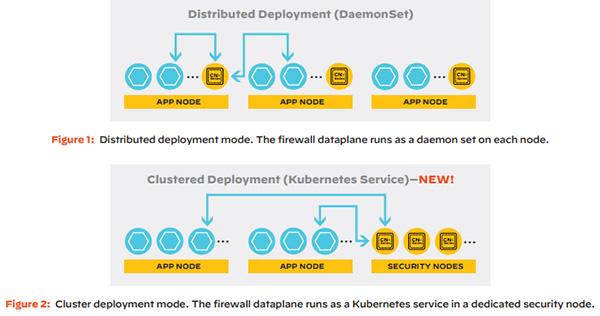
15. CN-Series Firewall for Kubernetes
15.1 Overview of CN-Series
15.1.1 Prevent Data Exfiltration from Kubernetes Environments
15.1.2 Prevent Lateral Spread of Threats Across Kubernetes Namespace Boundaries
15.2 CN-Series core concepts
以下列出使用 PAN-OS 的 PA 系列 Next Generation Firewall:
PA-220R Firewall
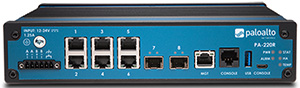
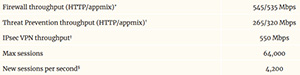
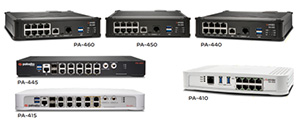
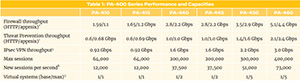
PA-400 Series Firewalls
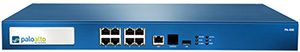
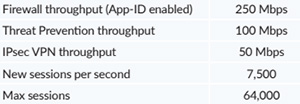
PA-500 Firewall
PA-800 Series Firewalls
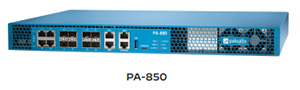
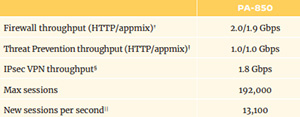
PA-1400 Series Firewalls
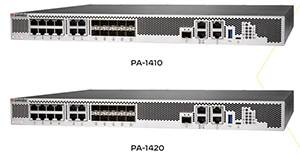
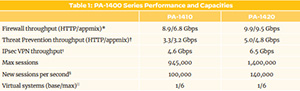
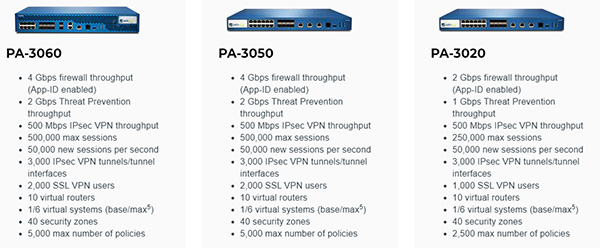
PA-3000 Series Firewalls
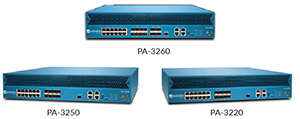
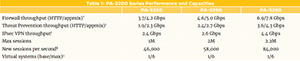
PA-3200 Series Firewalls
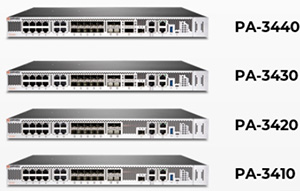
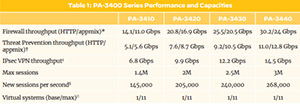
PA-3400 Series Firewalls
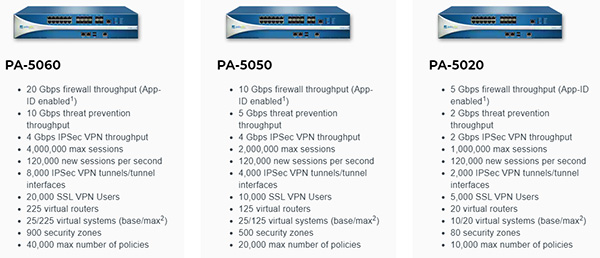
PA-5000 Series Firewalls
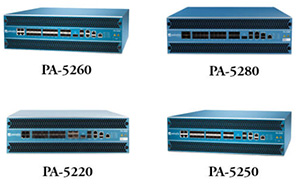
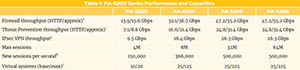
PA-5200 Series Firewalls
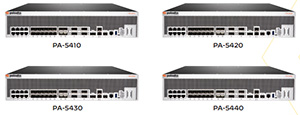
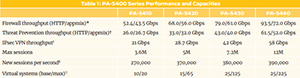
PA-5400 Series Firewalls
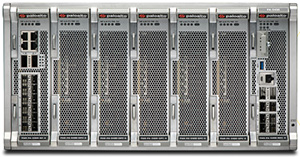
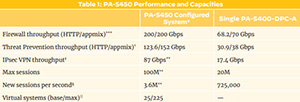
PA-5450 Firewall
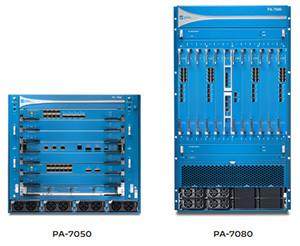
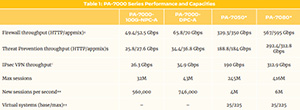
PA-7000 Series Firewalls
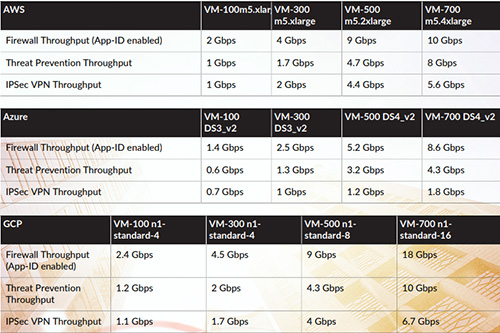
VM (Virtual Machine) Series Firewalls
CN (Container) Series Firewall